
Up to7×cheaper
than a traditional mobile pentest
ASCA is an autonomous mobile pentesting platform for iOS and Android apps. It finds exploitable vulnerabilities across your app and delivers premium pentest-level results in a fraction of the time.
than a traditional mobile pentest
Launch a pentest anytime. No scoping calls, no scheduling.
From upload to report, with evidence for every finding
Our agents work through your app the way a security researcher would.
ASCA runs a team of AI agents against your app on a dedicated emulator. They follow a pentester's method: map the attack surface, form hypotheses, write exploits, and keep only what they can prove.
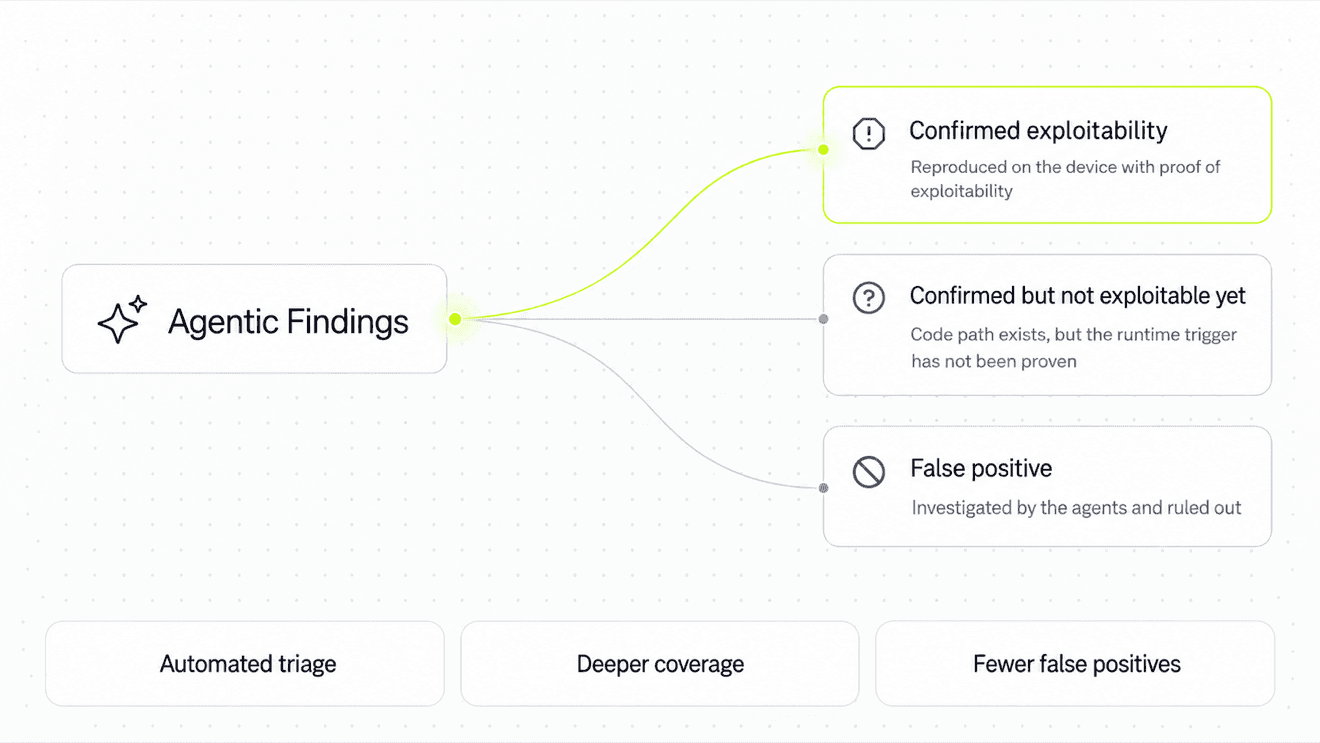
A scanner flags a vulnerability and stops there. ASCA tells you what is at risk, how serious it is, and how to fix it, in terms your developers can act on right away.
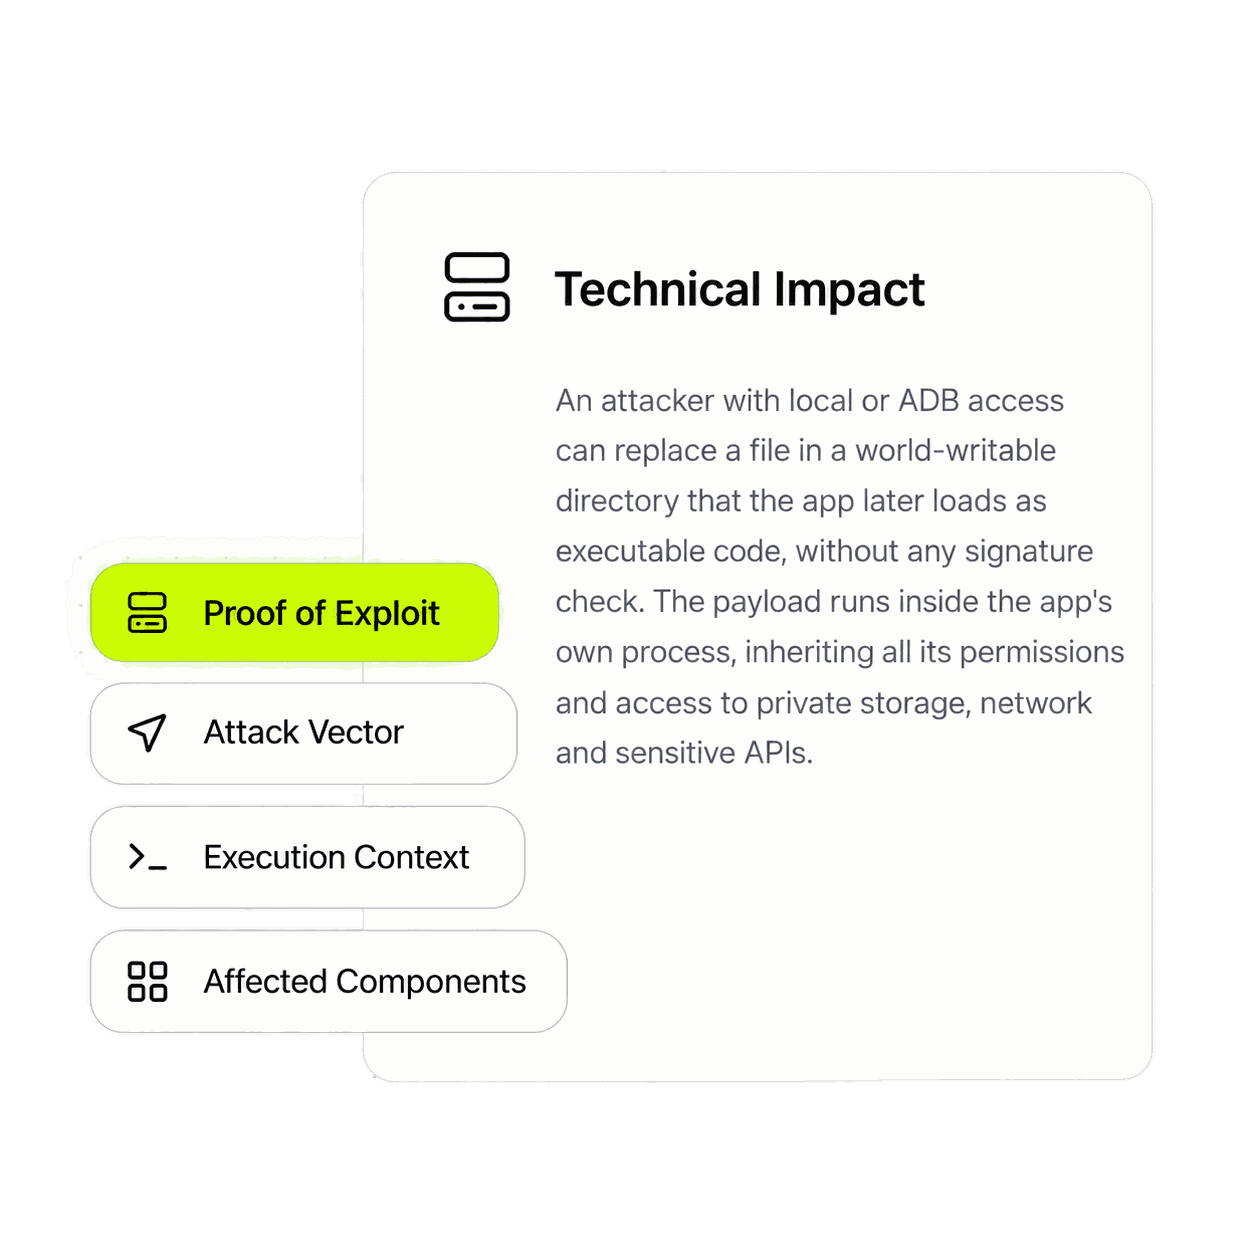
What happens at the system level: which data is exposed, which operations are affected
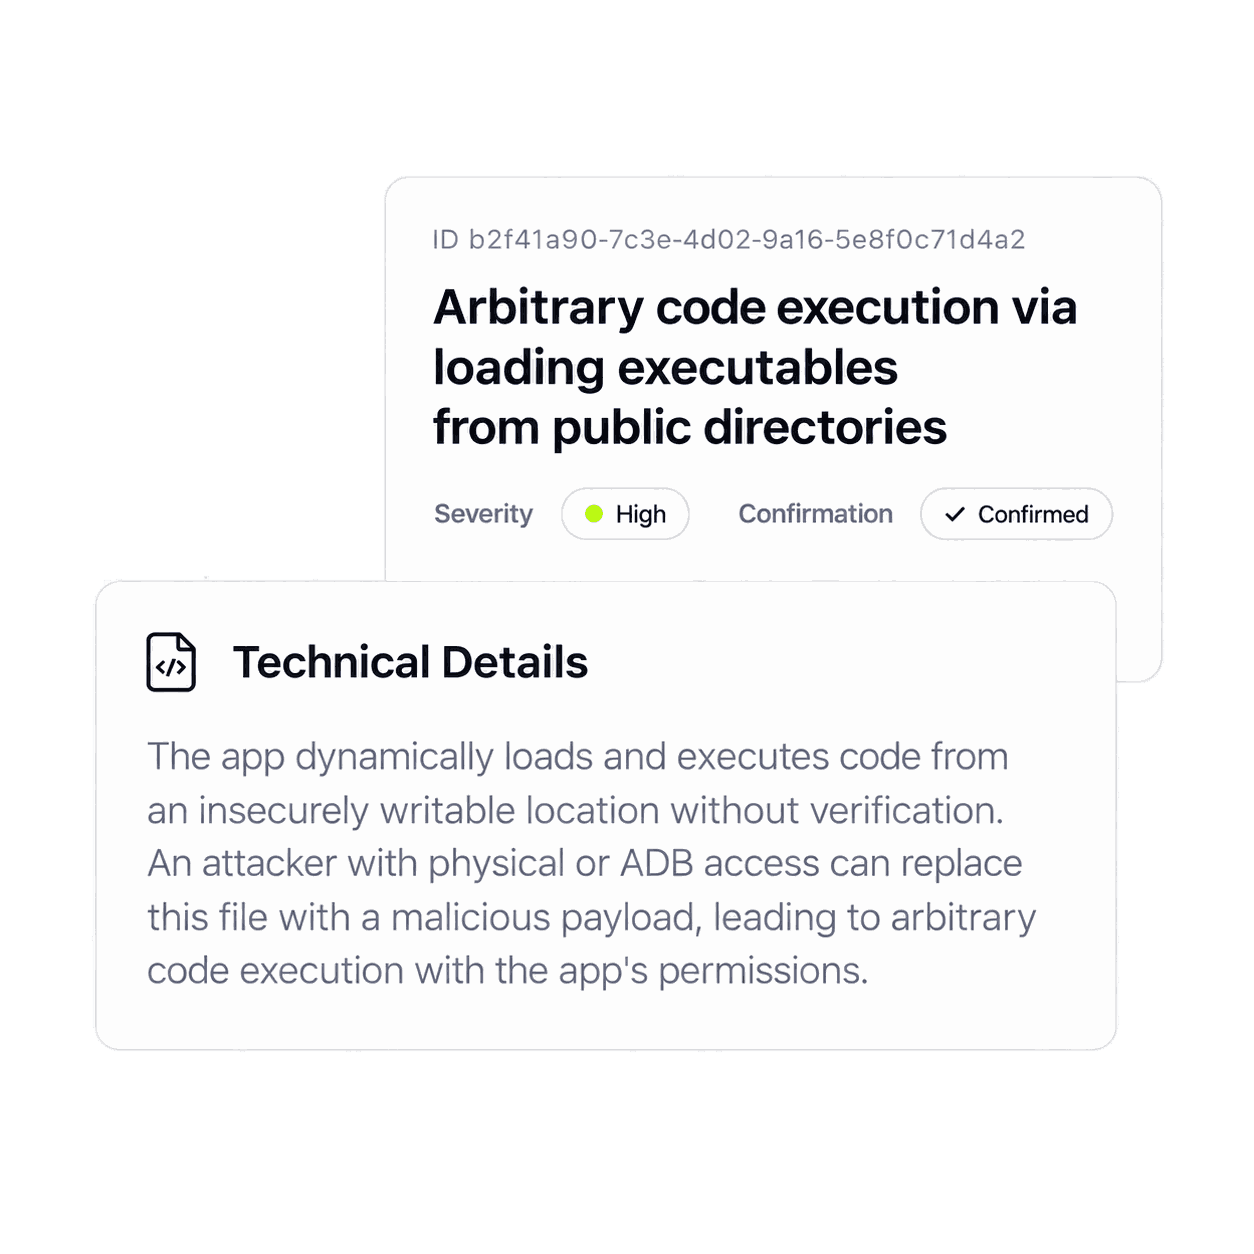
How the vulnerability works in this specific code, with the relevant execution path
Concrete remediation guidance, specific to the code and context — not a generic reference to a standard
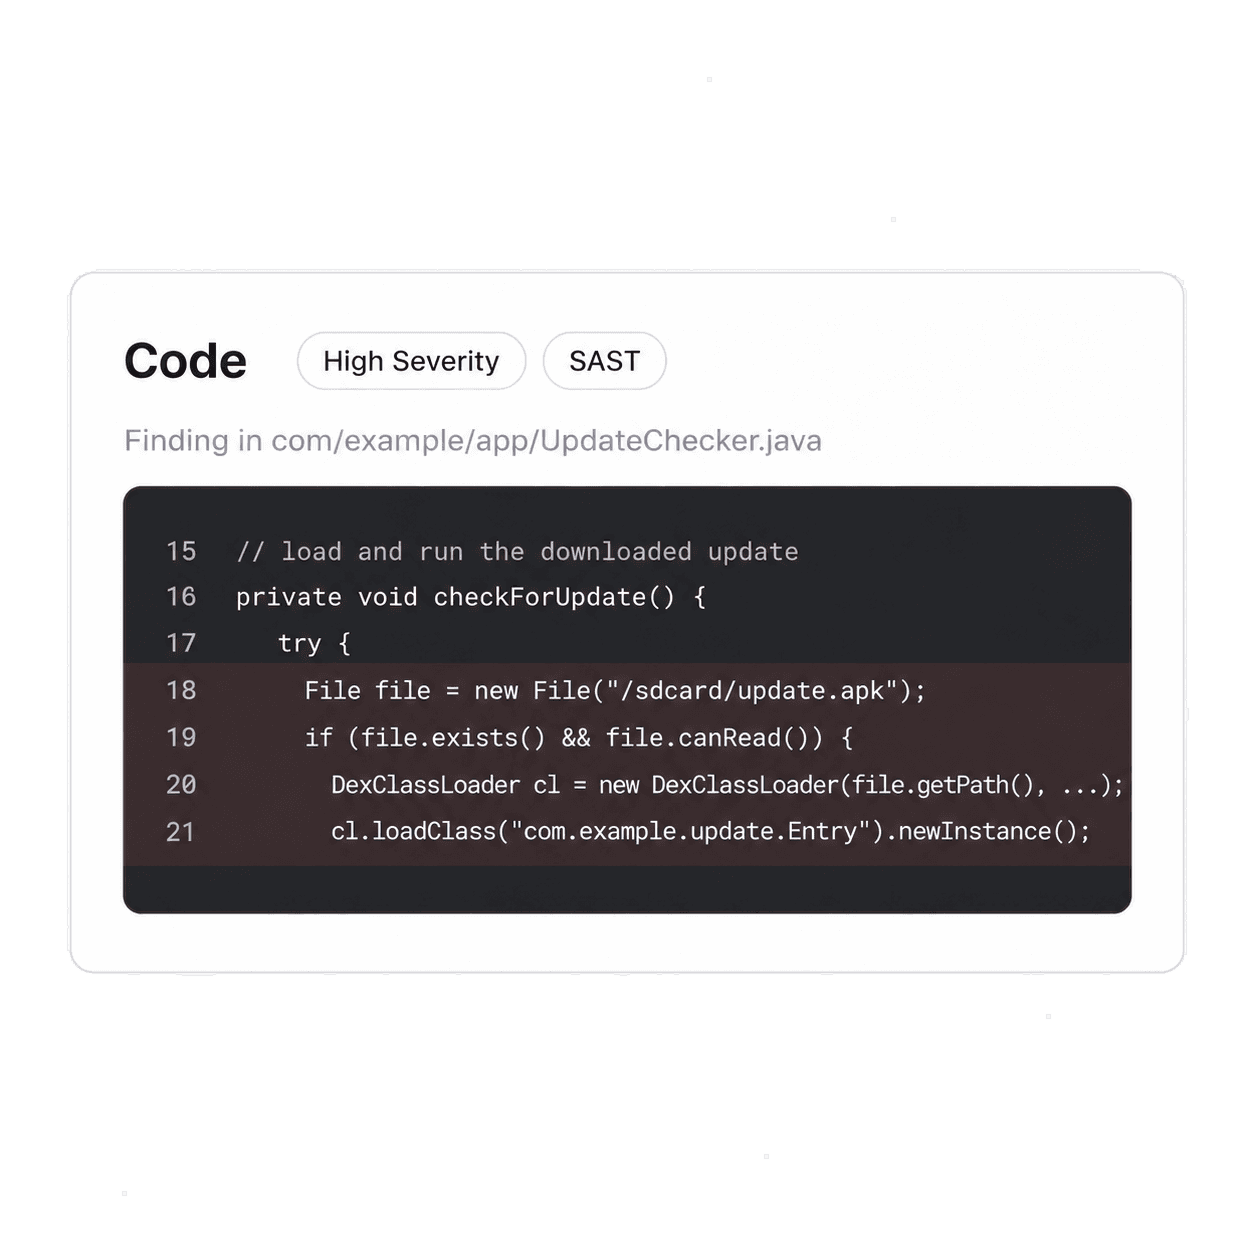
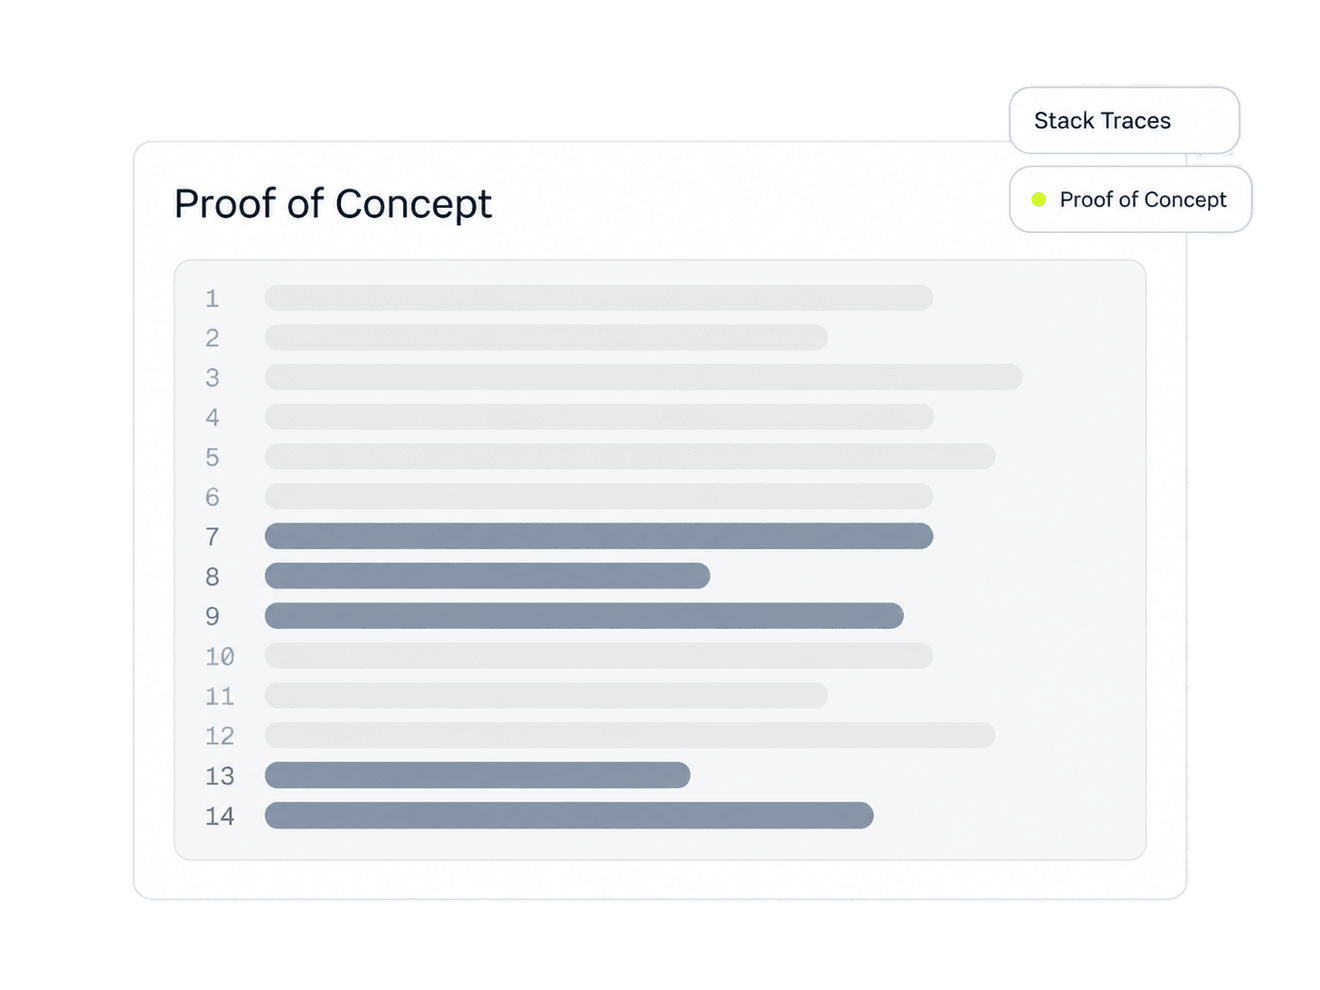
The relevant lines of code, highlighted
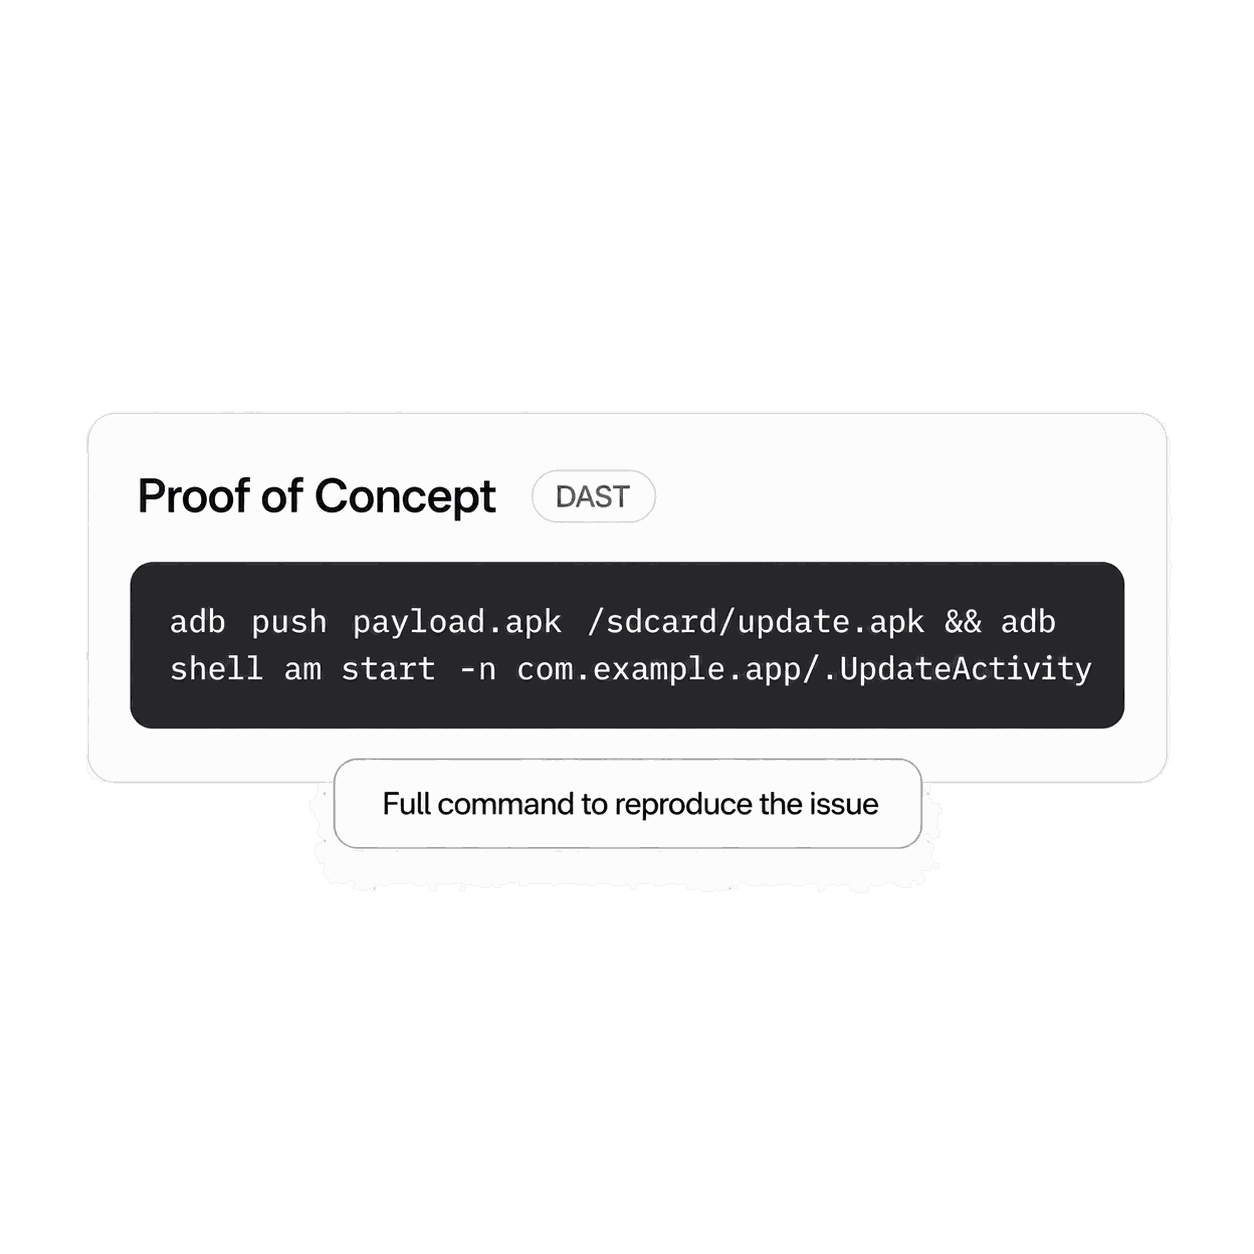
Full command, deeplink payload, or exploit code to reproduce the issue
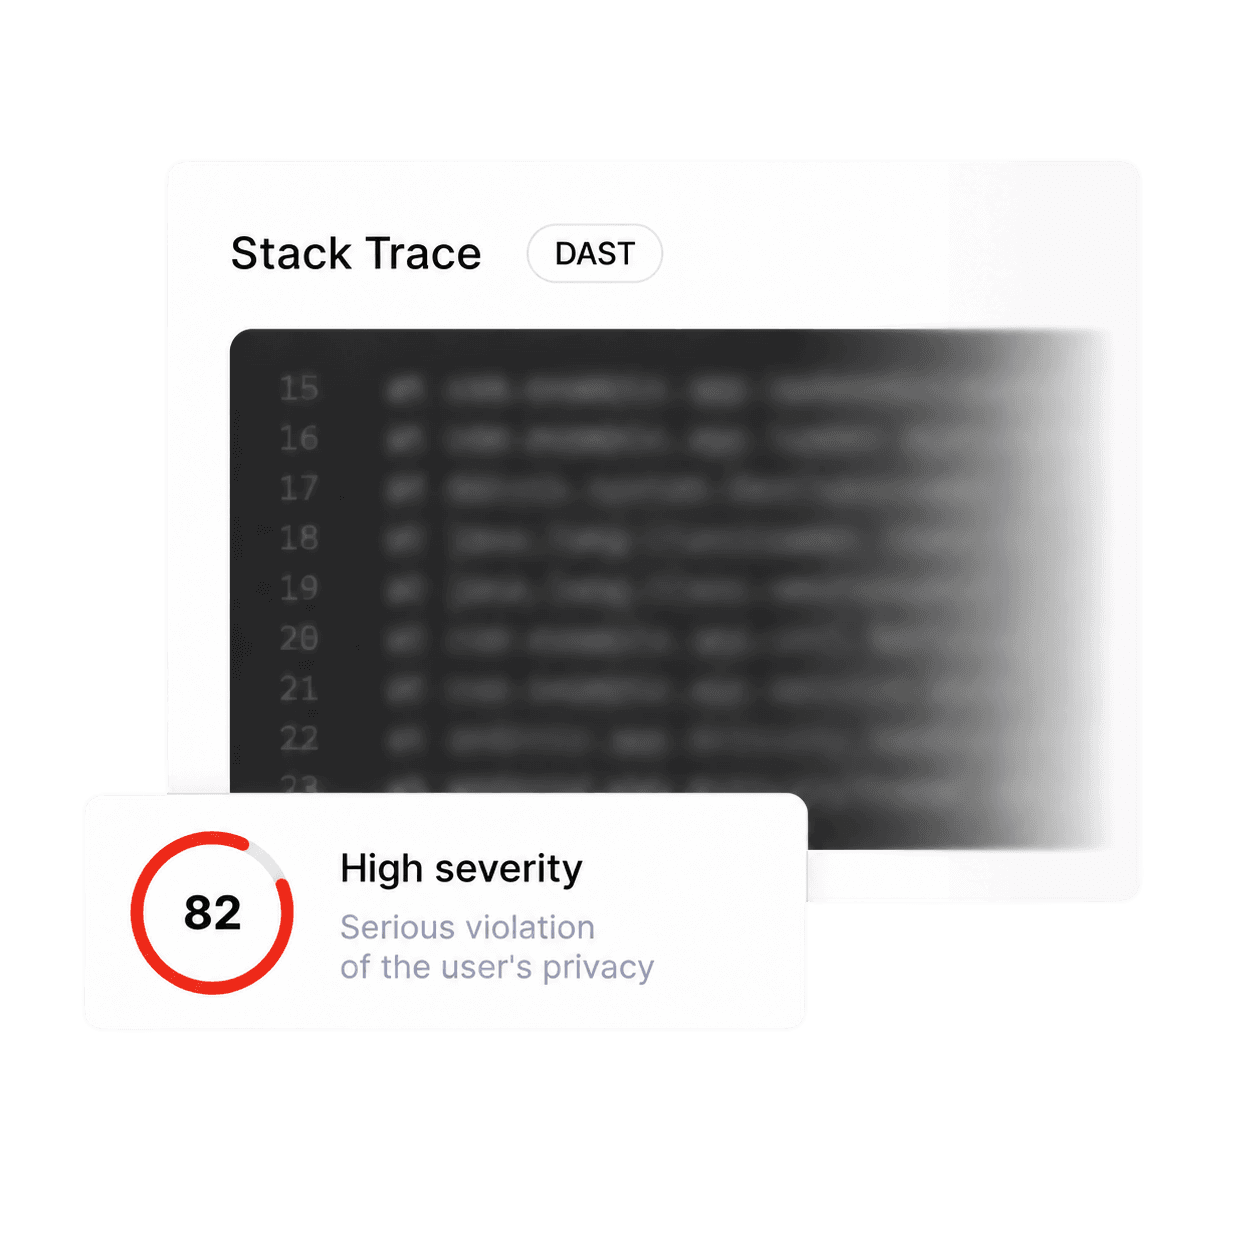
The exact call chain from the entry point to the vulnerable operation, so you can follow it in your own code
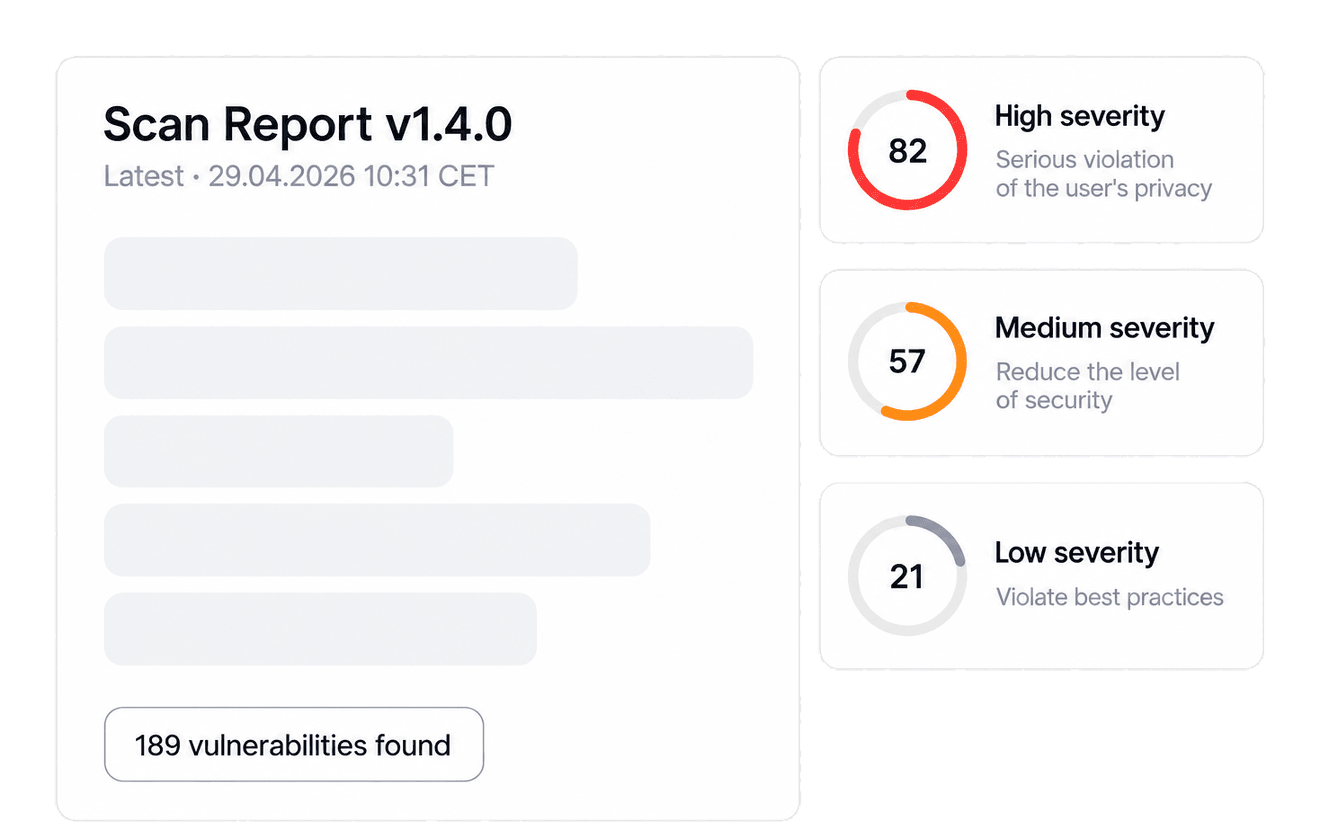
Upload your APK, no source code required. 30+ specialized agents read your app the way an auditor would, following untrusted input from its entry point to the sensitive operation it can reach. Every lead comes with the affected code, its severity and its impact.
Every lead is then tested against your app running on a dedicated emulator, with crafted deep links, intents and inputs. You know which vulnerabilities are actually exploitable and get a proof of concept with clear reproduction steps. Root detection and certificate pinning are handled for you.
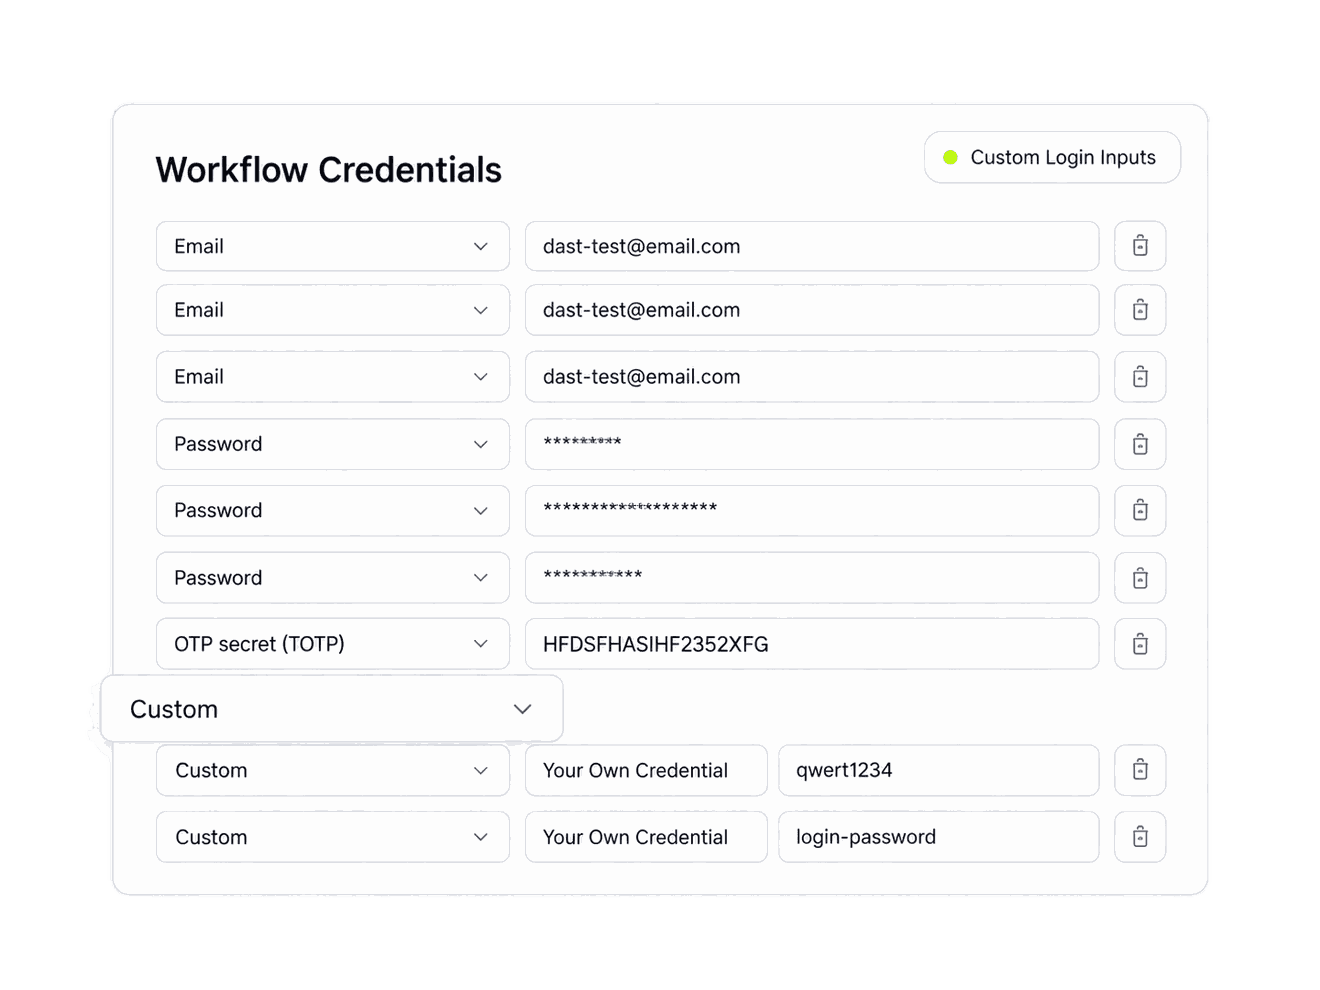
Give ASCA a test account and the agents log in to test what your users actually reach: payments, account settings, private content. Each session is recorded, so you can watch what the agents did.
ASCA's agents investigate each finding like a pentester would: they trace the attack path, write the exploit and run it against your app. Only what they could prove reaches your report, as a bug bounty-style finding with its proof of concept and how to fix it.
Most scanners flag dangerous functions. ASCA's agents check whether attacker-controlled data can actually reach them, then prove it on the running app.
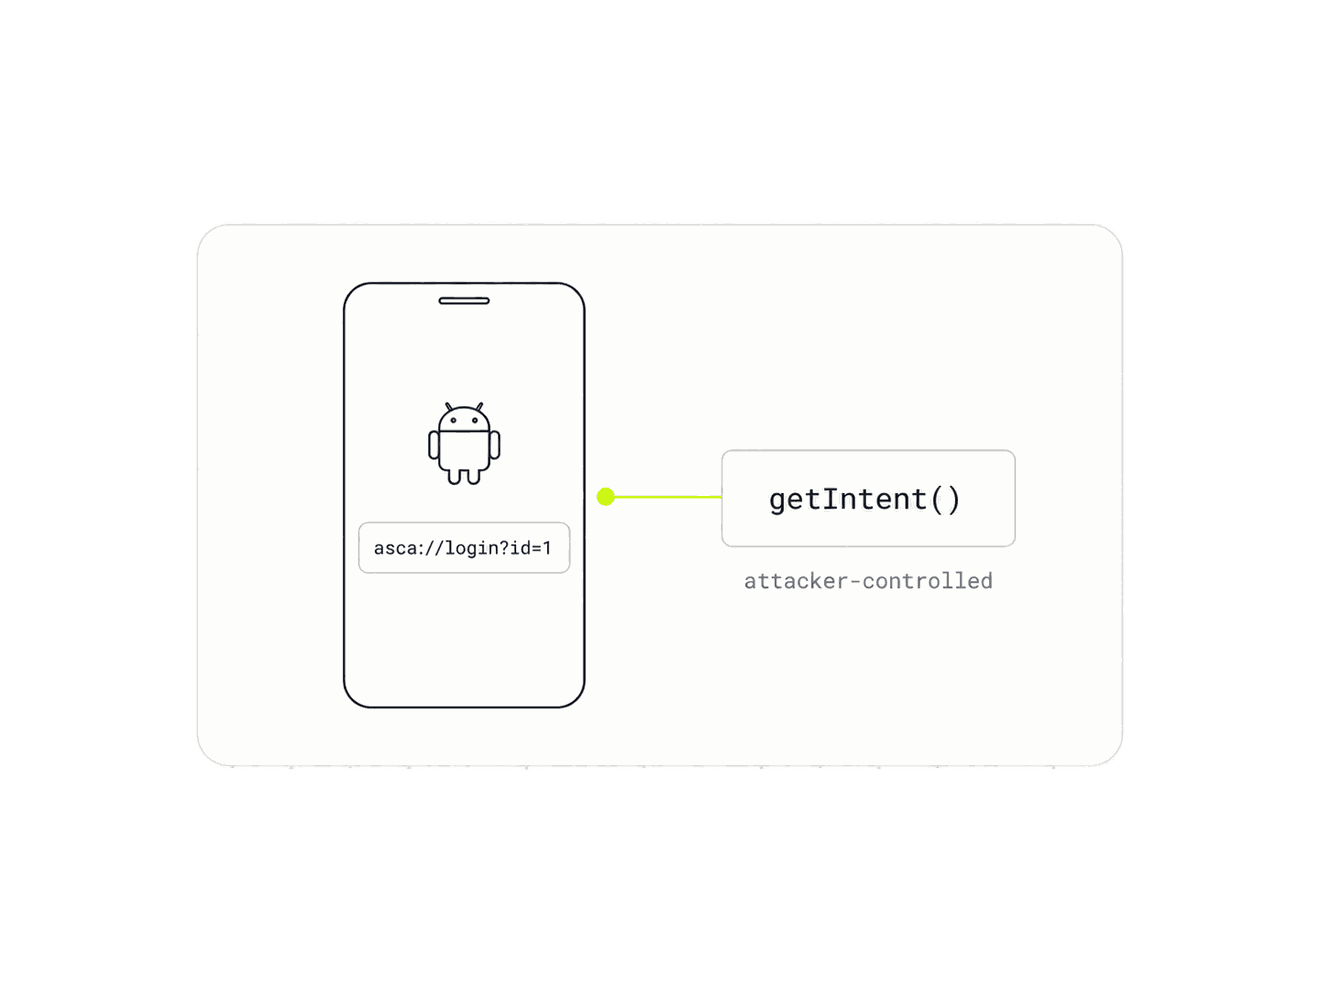
01
Where attacker-controlled data enters your app: an intent, a deep link, a file.
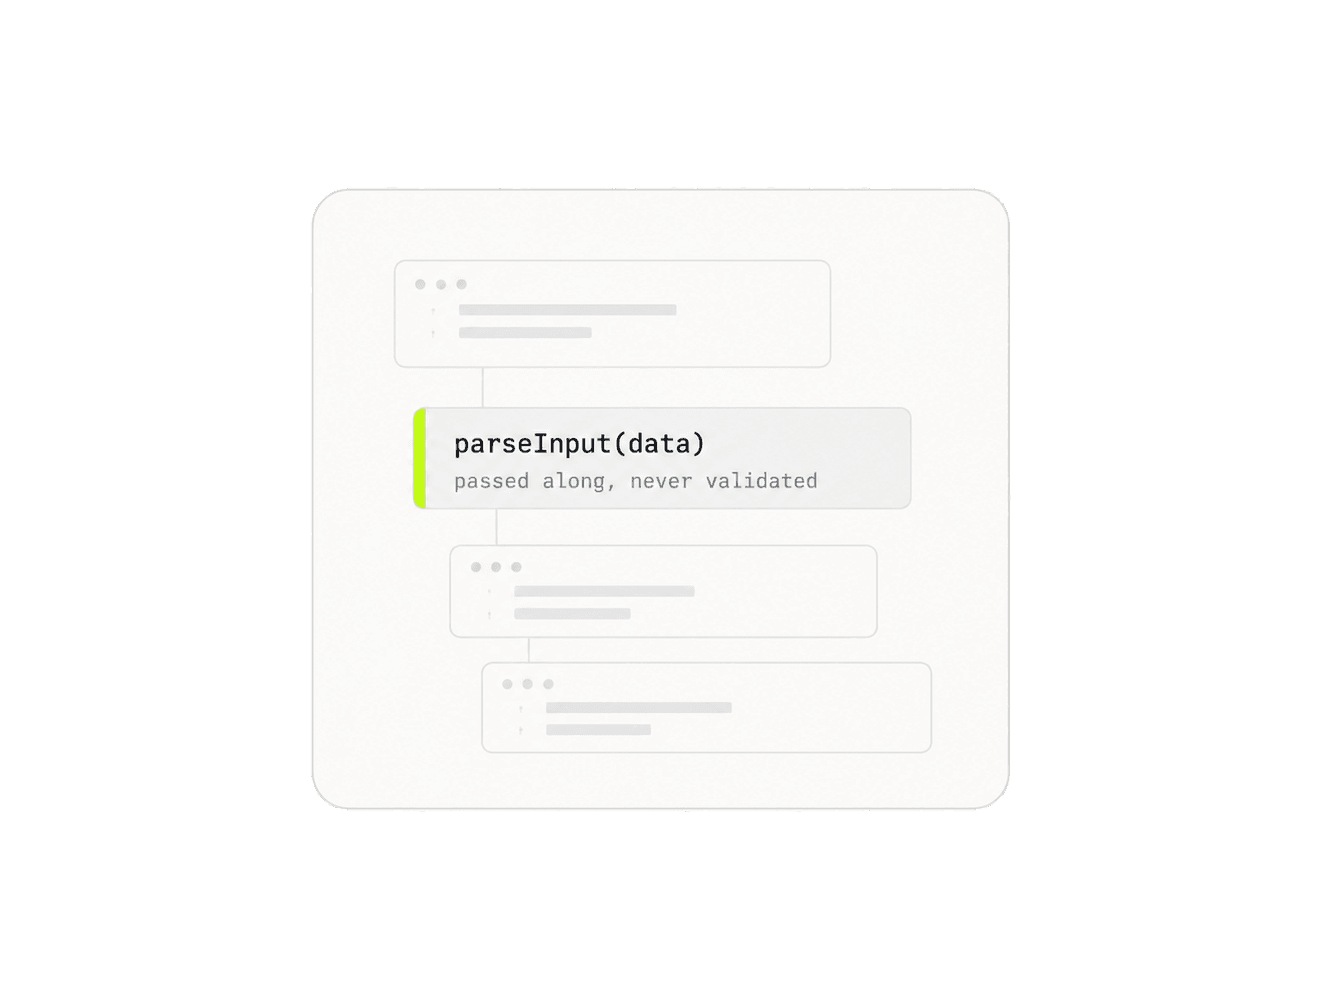
02
The agents follow that data through your code, across methods and components.
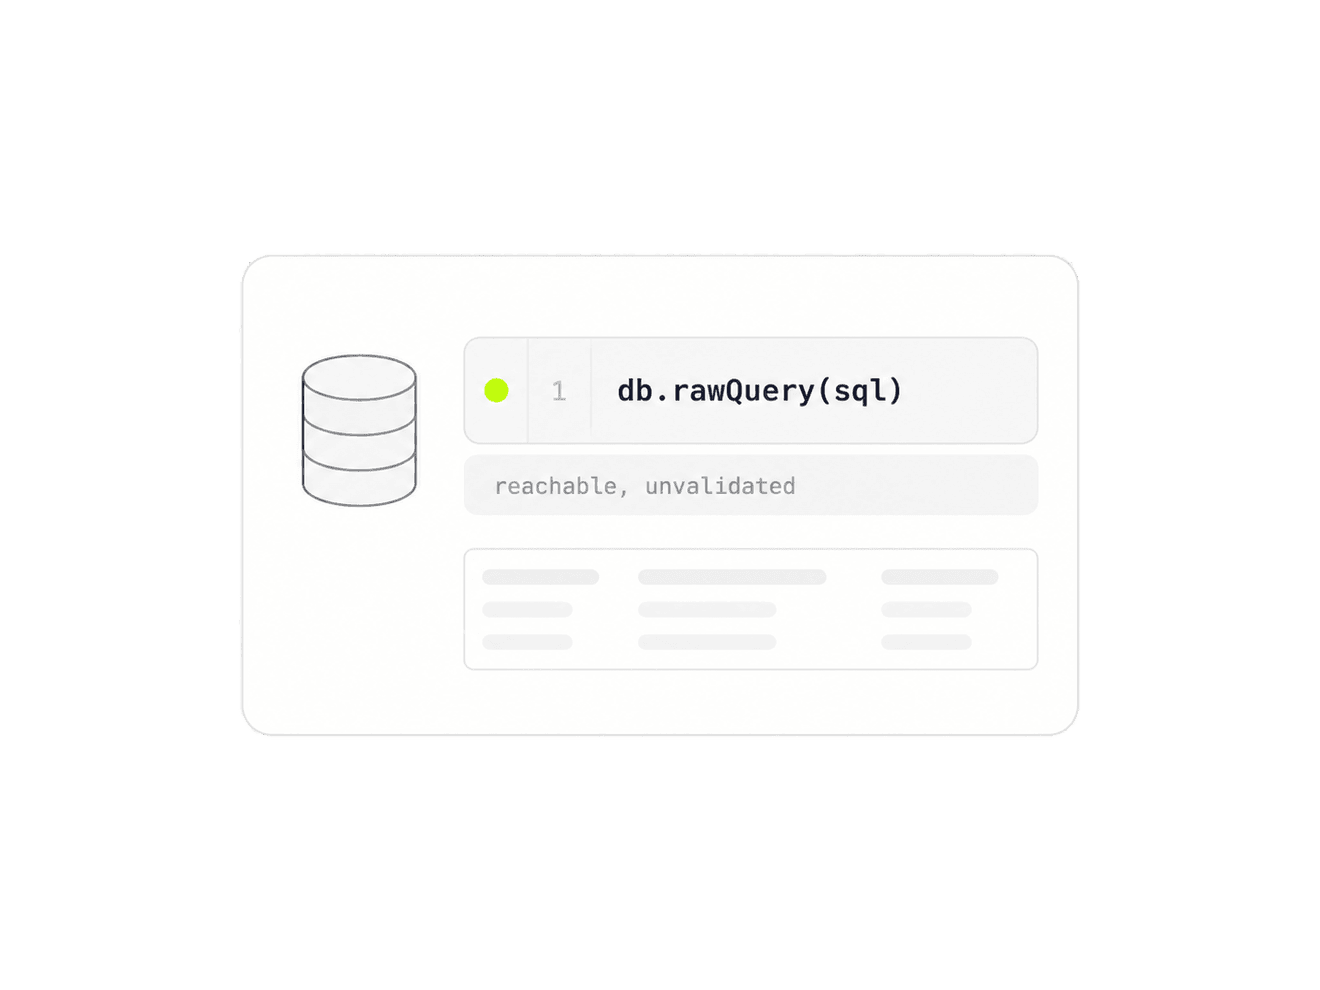
03
They check whether it reaches a sensitive operation without being validated.
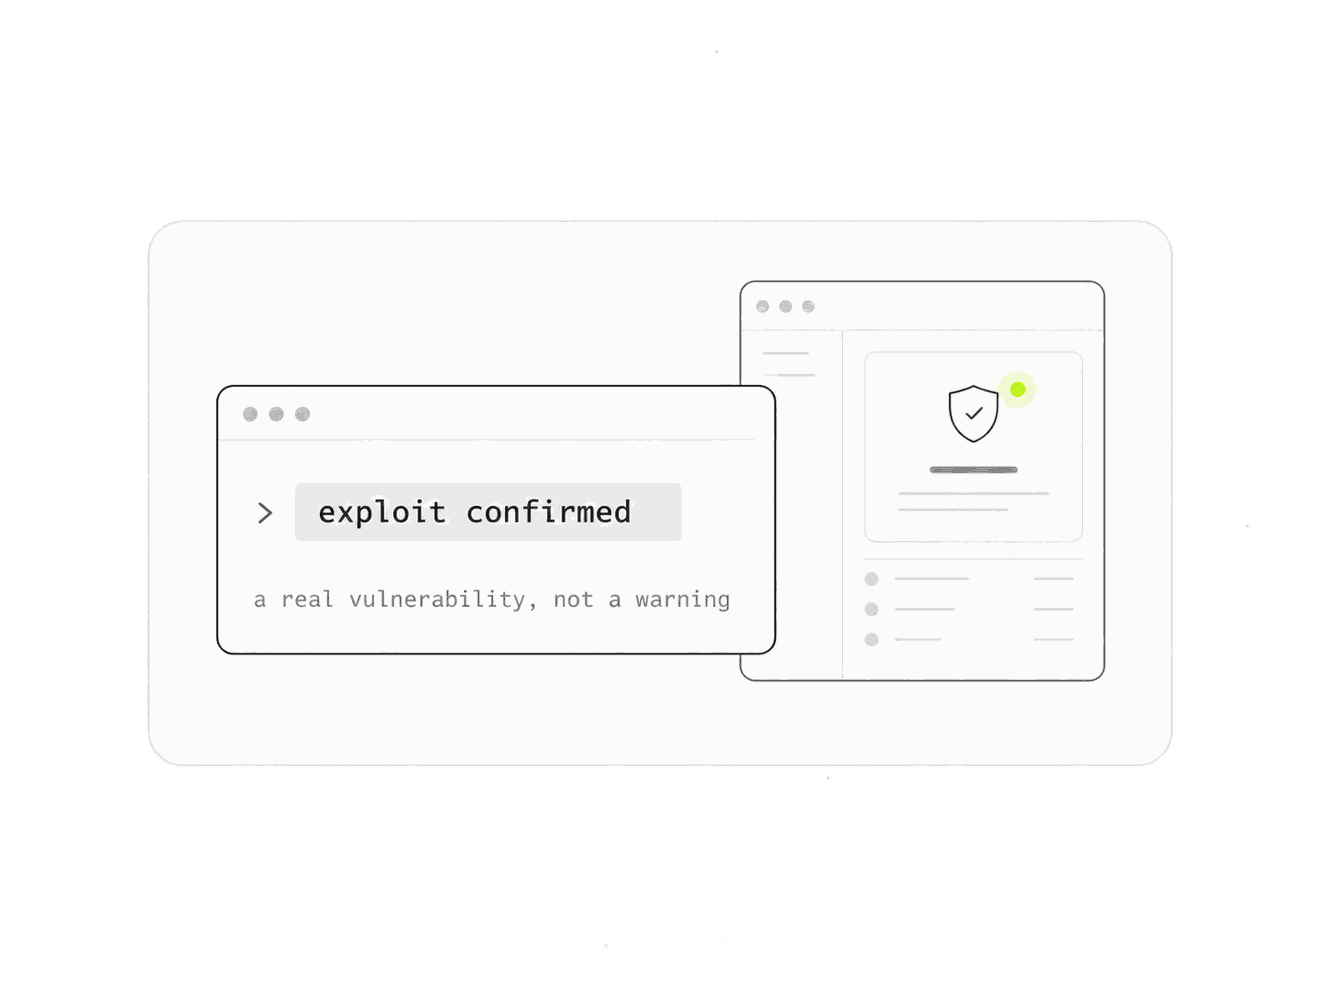
04
The path is then tested on the running app, so you know it is exploitable, not just possible.
05
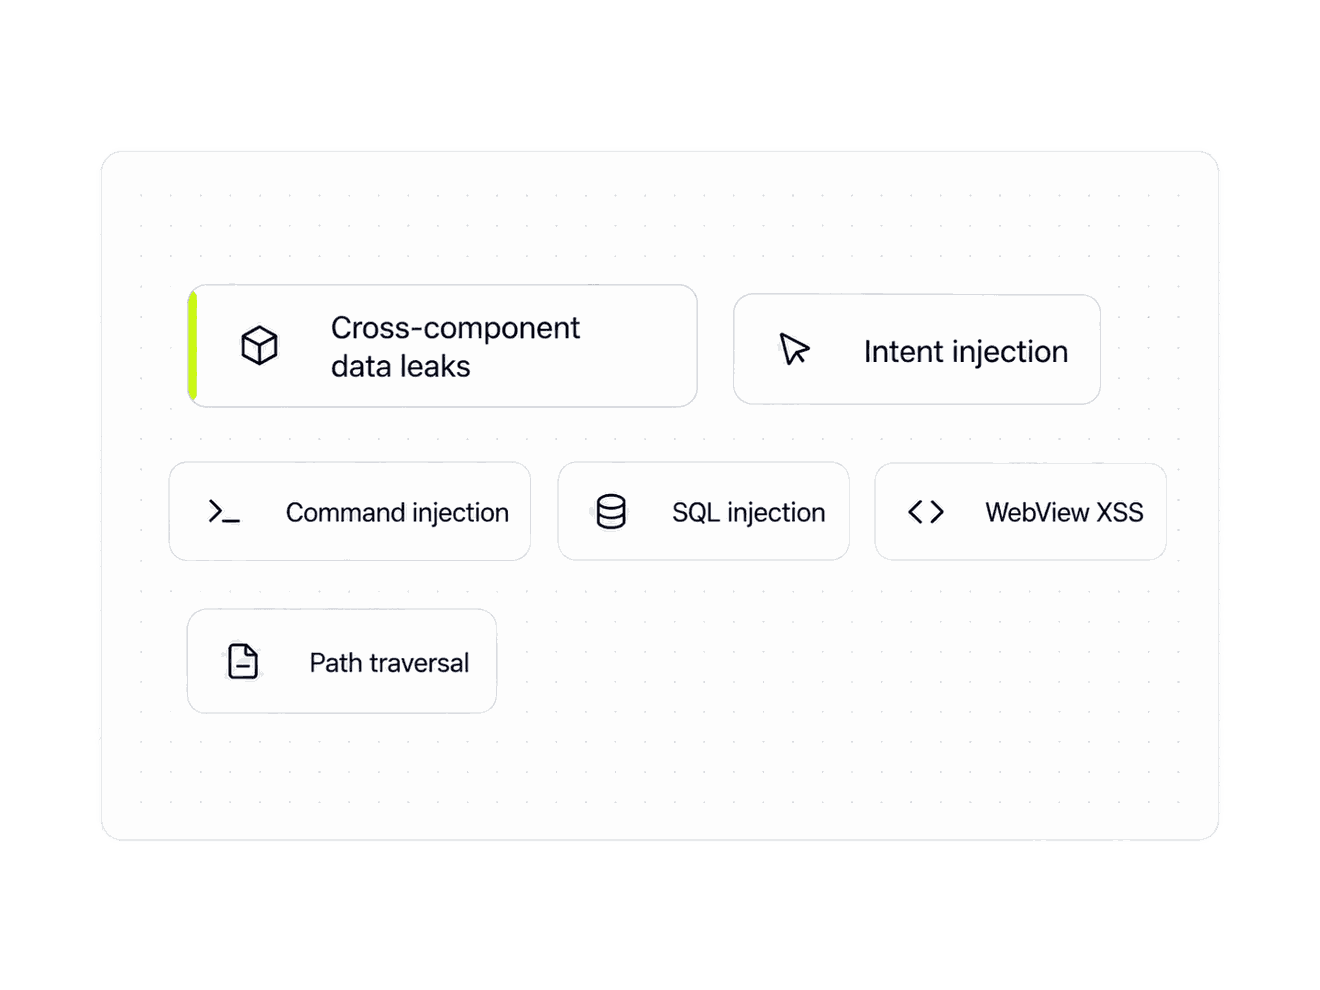
Cross-component data leaks, intent injection, command injection, SQL injection, WebView XSS, path traversal, SSRF.
06
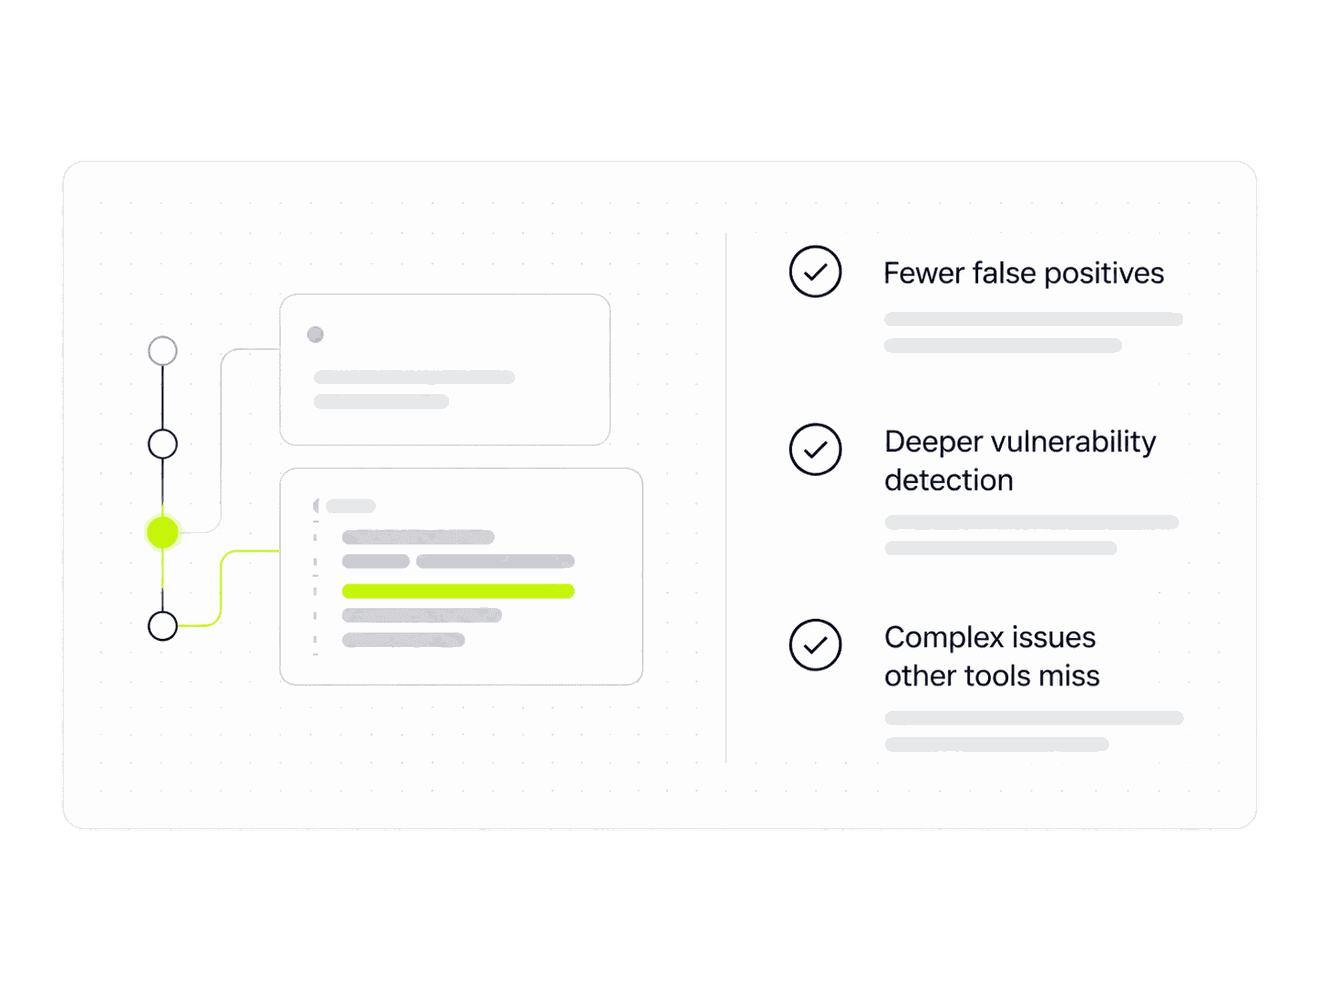
Pattern matching creates noise. ASCA follows the full data path, then tests it on a real device: fewer false positives, deeper detection, complex issues other tools miss.
Mobile pentesting that is faster, cheaper and continuous, with evidence for every finding.
5h
Replacement of manual pentesting process that previously took five days
No scoping calls, no scheduling. Upload your app and the pentest starts.
On demand
30+
Specialized agents, each focused on one class of Android vulnerability
Every finding comes with a proof of concept, so your developers fix real risks instead of debating alerts.
Evidence
5h
Replacement of manual pentesting process that previously took five days
No scoping calls, no scheduling. Upload your app and the pentest starts.
On demand
30+
Specialized agents, each focused on one class of Android vulnerability
Every finding comes with a proof of concept, so your developers fix real risks instead of debating alerts.
Evidence
5h
Replacement of manual pentesting process that previously took five days
No scoping calls, no scheduling. Upload your app and the pentest starts.
On demand
30+
Specialized agents, each focused on one class of Android vulnerability
Every finding comes with a proof of concept, so your developers fix real risks instead of debating alerts.
Evidence
5h
Replacement of manual pentesting process that previously took five days
No scoping calls, no scheduling. Upload your app and the pentest starts.
On demand
30+
Specialized agents, each focused on one class of Android vulnerability
Every finding comes with a proof of concept, so your developers fix real risks instead of debating alerts.
Evidence
393% ROI
Of a security testing process for a head of AppSec & offensive security team
6
Pieces of evidence in every finding, from technical impact to stack trace
No source code required. ASCA works on the compiled app, the way an external attacker would.
Black box
12
Saved per security engineer per month
393% ROI
Of a security testing process for a head of AppSec & offensive security team
6
Pieces of evidence in every finding, from technical impact to stack trace
No source code required. ASCA works on the compiled app, the way an external attacker would.
Black box
12
Saved per security engineer per month
393% ROI
Of a security testing process for a head of AppSec & offensive security team
6
Pieces of evidence in every finding, from technical impact to stack trace
No source code required. ASCA works on the compiled app, the way an external attacker would.
Black box
12
Saved per security engineer per month
393% ROI
Of a security testing process for a head of AppSec & offensive security team
6
Pieces of evidence in every finding, from technical impact to stack trace
No source code required. ASCA works on the compiled app, the way an external attacker would.
Black box
12
Saved per security engineer per month
An open API and real-time webhooks. Use ASCA at scale, within your own ecosystem.
Create, manage, and track thousands of links programmatically. Integrate ASCA into your product, workflows, and automations.
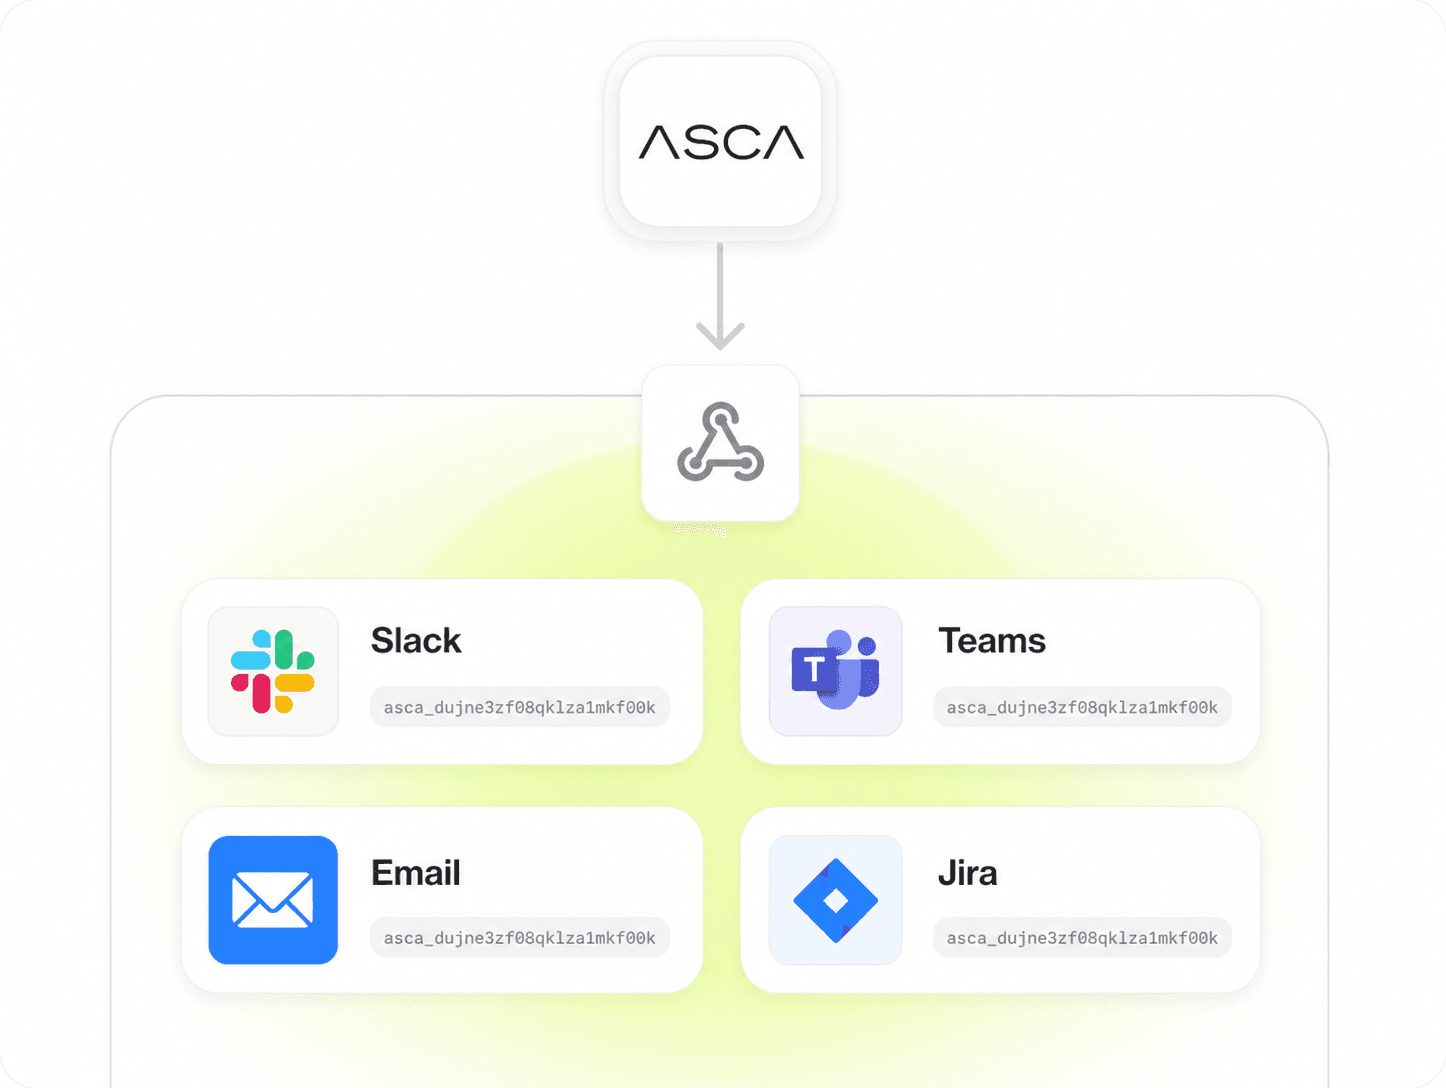
Get notified as soon as something happens: a critical vulnerability, a scan completed. Send the data to wherever you need it, instantly.
Native or cross-platform, ASCA detects how your app was built and reads the framework's own code, not just the thin native layer.


Don't let your vulnerabilities escape.
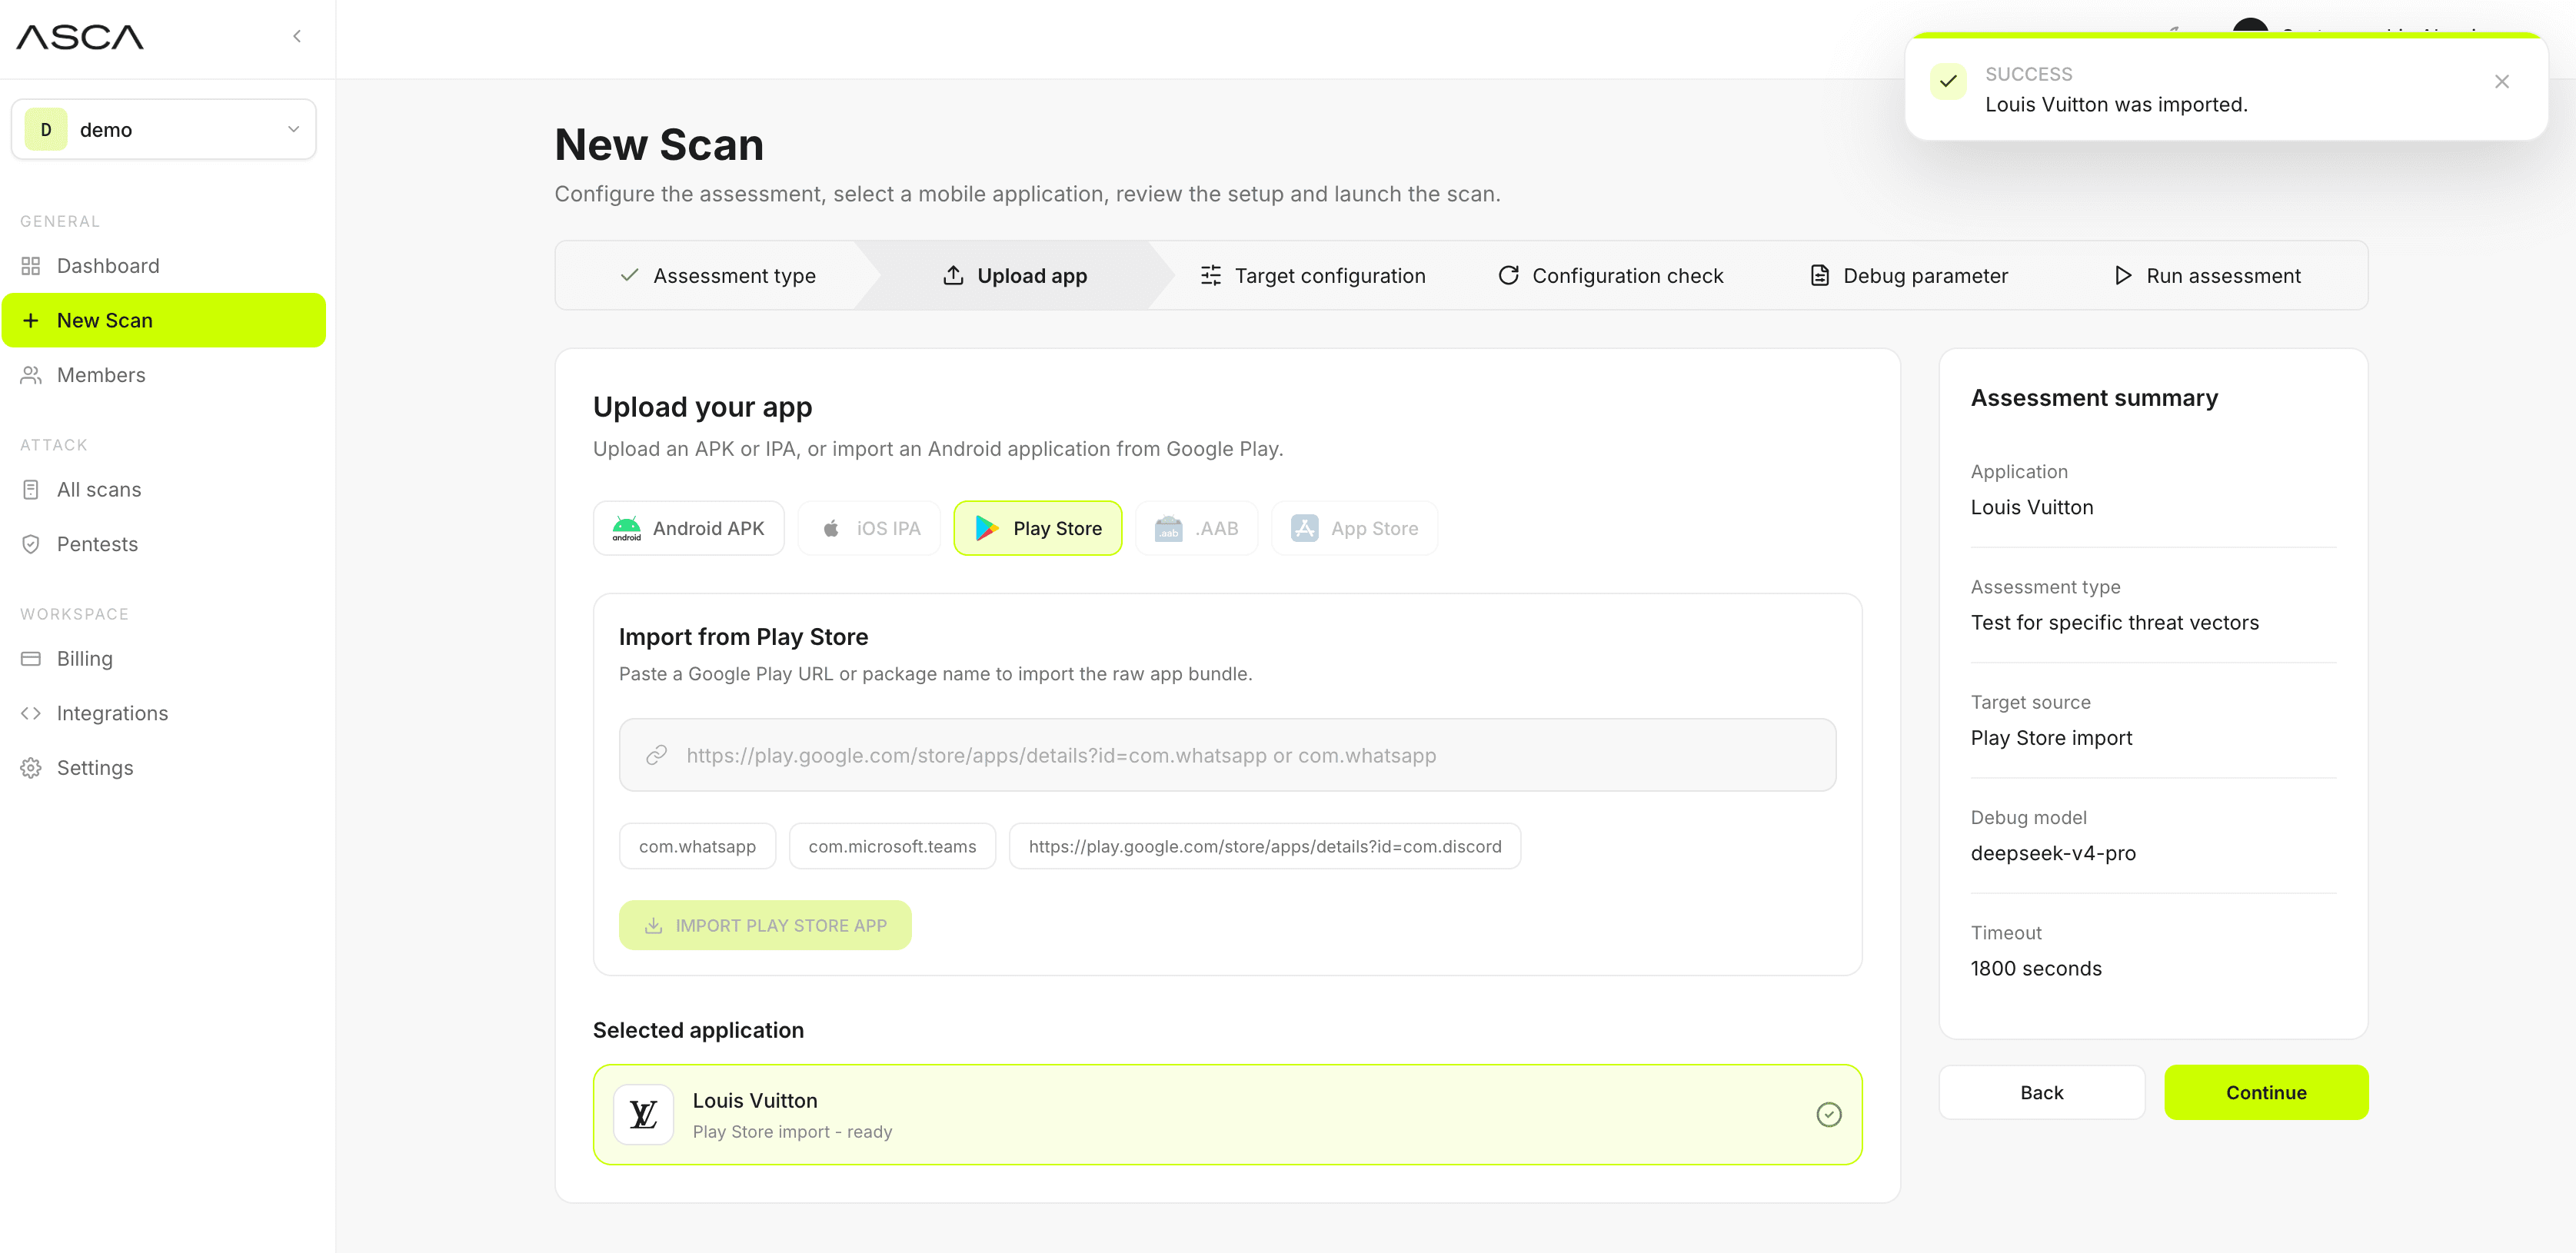
Upload your APK or import your app from Google Play. ASCA's agents decompile it, map its attack surface and follow untrusted input from each entry point to the sensitive operation it can reach. Every confirmed issue comes with a full report.
No. ASCA works on the compiled application, the same way an external attacker would. You can still add documentation or source files in the scan settings if you want to give the agents more context.
Android apps today, whether native or built with Flutter, React Native or Cordova. ASCA detects the framework automatically and adapts its analysis. iOS support is on the way.
A static analysis usually completes in under 4 hours. You can follow the agents' progress live in the dashboard, and the report is available as soon as the scan ends.
Each finding comes with its technical impact, how the vulnerability works in your code, how to fix it, the relevant code snippet, a proof of concept and the full stack trace from the entry point to the vulnerable operation.
ASCA is free while the public beta is open. Create an account, upload your app and start a scan, no credit card required.